Iranian state actors targeting UK dissidents, activists and journalists with spyware
Por Bryony Gooch — – World RSS Feed
Iranian state actors targeting UK dissidents, activists and journalists with spyware
Iranian agents used social engineering tricks such as fake MRI test results to lure victims in, the NCSC said
Bryony Gooch Tuesday 15 September 2026 19:17 BST
- Bookmark
- Comments Go to comments
Bookmark popover
Removed from bookmarks
Close popover
Your support helps us to tell the story
Read more Support Now
From reproductive rights to climate change to Big Tech, The Independent is on the ground when the story is developing. Whether it’s investigating the financials of Elon Musk’s pro-Trump PAC or producing our latest documentary, ‘The A Word’, which shines a light on the American women fighting for reproductive rights, we know how important it is to parse out the facts from the messaging.
At such a critical moment in US history, we need reporters on the ground. Your donation allows us to keep sending journalists to speak to both sides of the story.
The Independent is trusted by Americans across the entire political spectrum. And unlike many other quality news outlets, we choose not to lock Americans out of our reporting and analysis with paywalls. We believe quality journalism should be available to everyone, paid for by those who can afford it.
Your support makes all the difference. Read more
British intelligence has issued a warning after finding Iranian spies have targeted dissidents with spyware that can enable tracking of their movements.
Dissidents, activists and journalists were targeted by state actors that impersonated their contacts on messaging apps to trick them into downloading spyware called Chosen Brick, the National Cyber Security Centre, part of GCHQ, warned.
The malware gave agents access to the person’s contacts, emails and social media messages as well as a device’s microphone and content on the screen.
 open image in gallery
The UK, alongside allies in the US and the Netherlands, discovered the plot which is targeting both British dissidents and others from a range of different countries. It remains unclear how many people were affected by the malware, although the FBI claimed that cyber actors had used the malware dating back to Autumn 2023.
Iranian agents used social engineering tricks to tailor their impersonations to areas of relevance or interest to their targets; in one instance, fake MRI test results lured a victim in.
The malware, targeting Windows operating systems, will survive a device being rebooted. Some stolen personal details have been posted on pro-Iranian leak sites, the NCSC said.
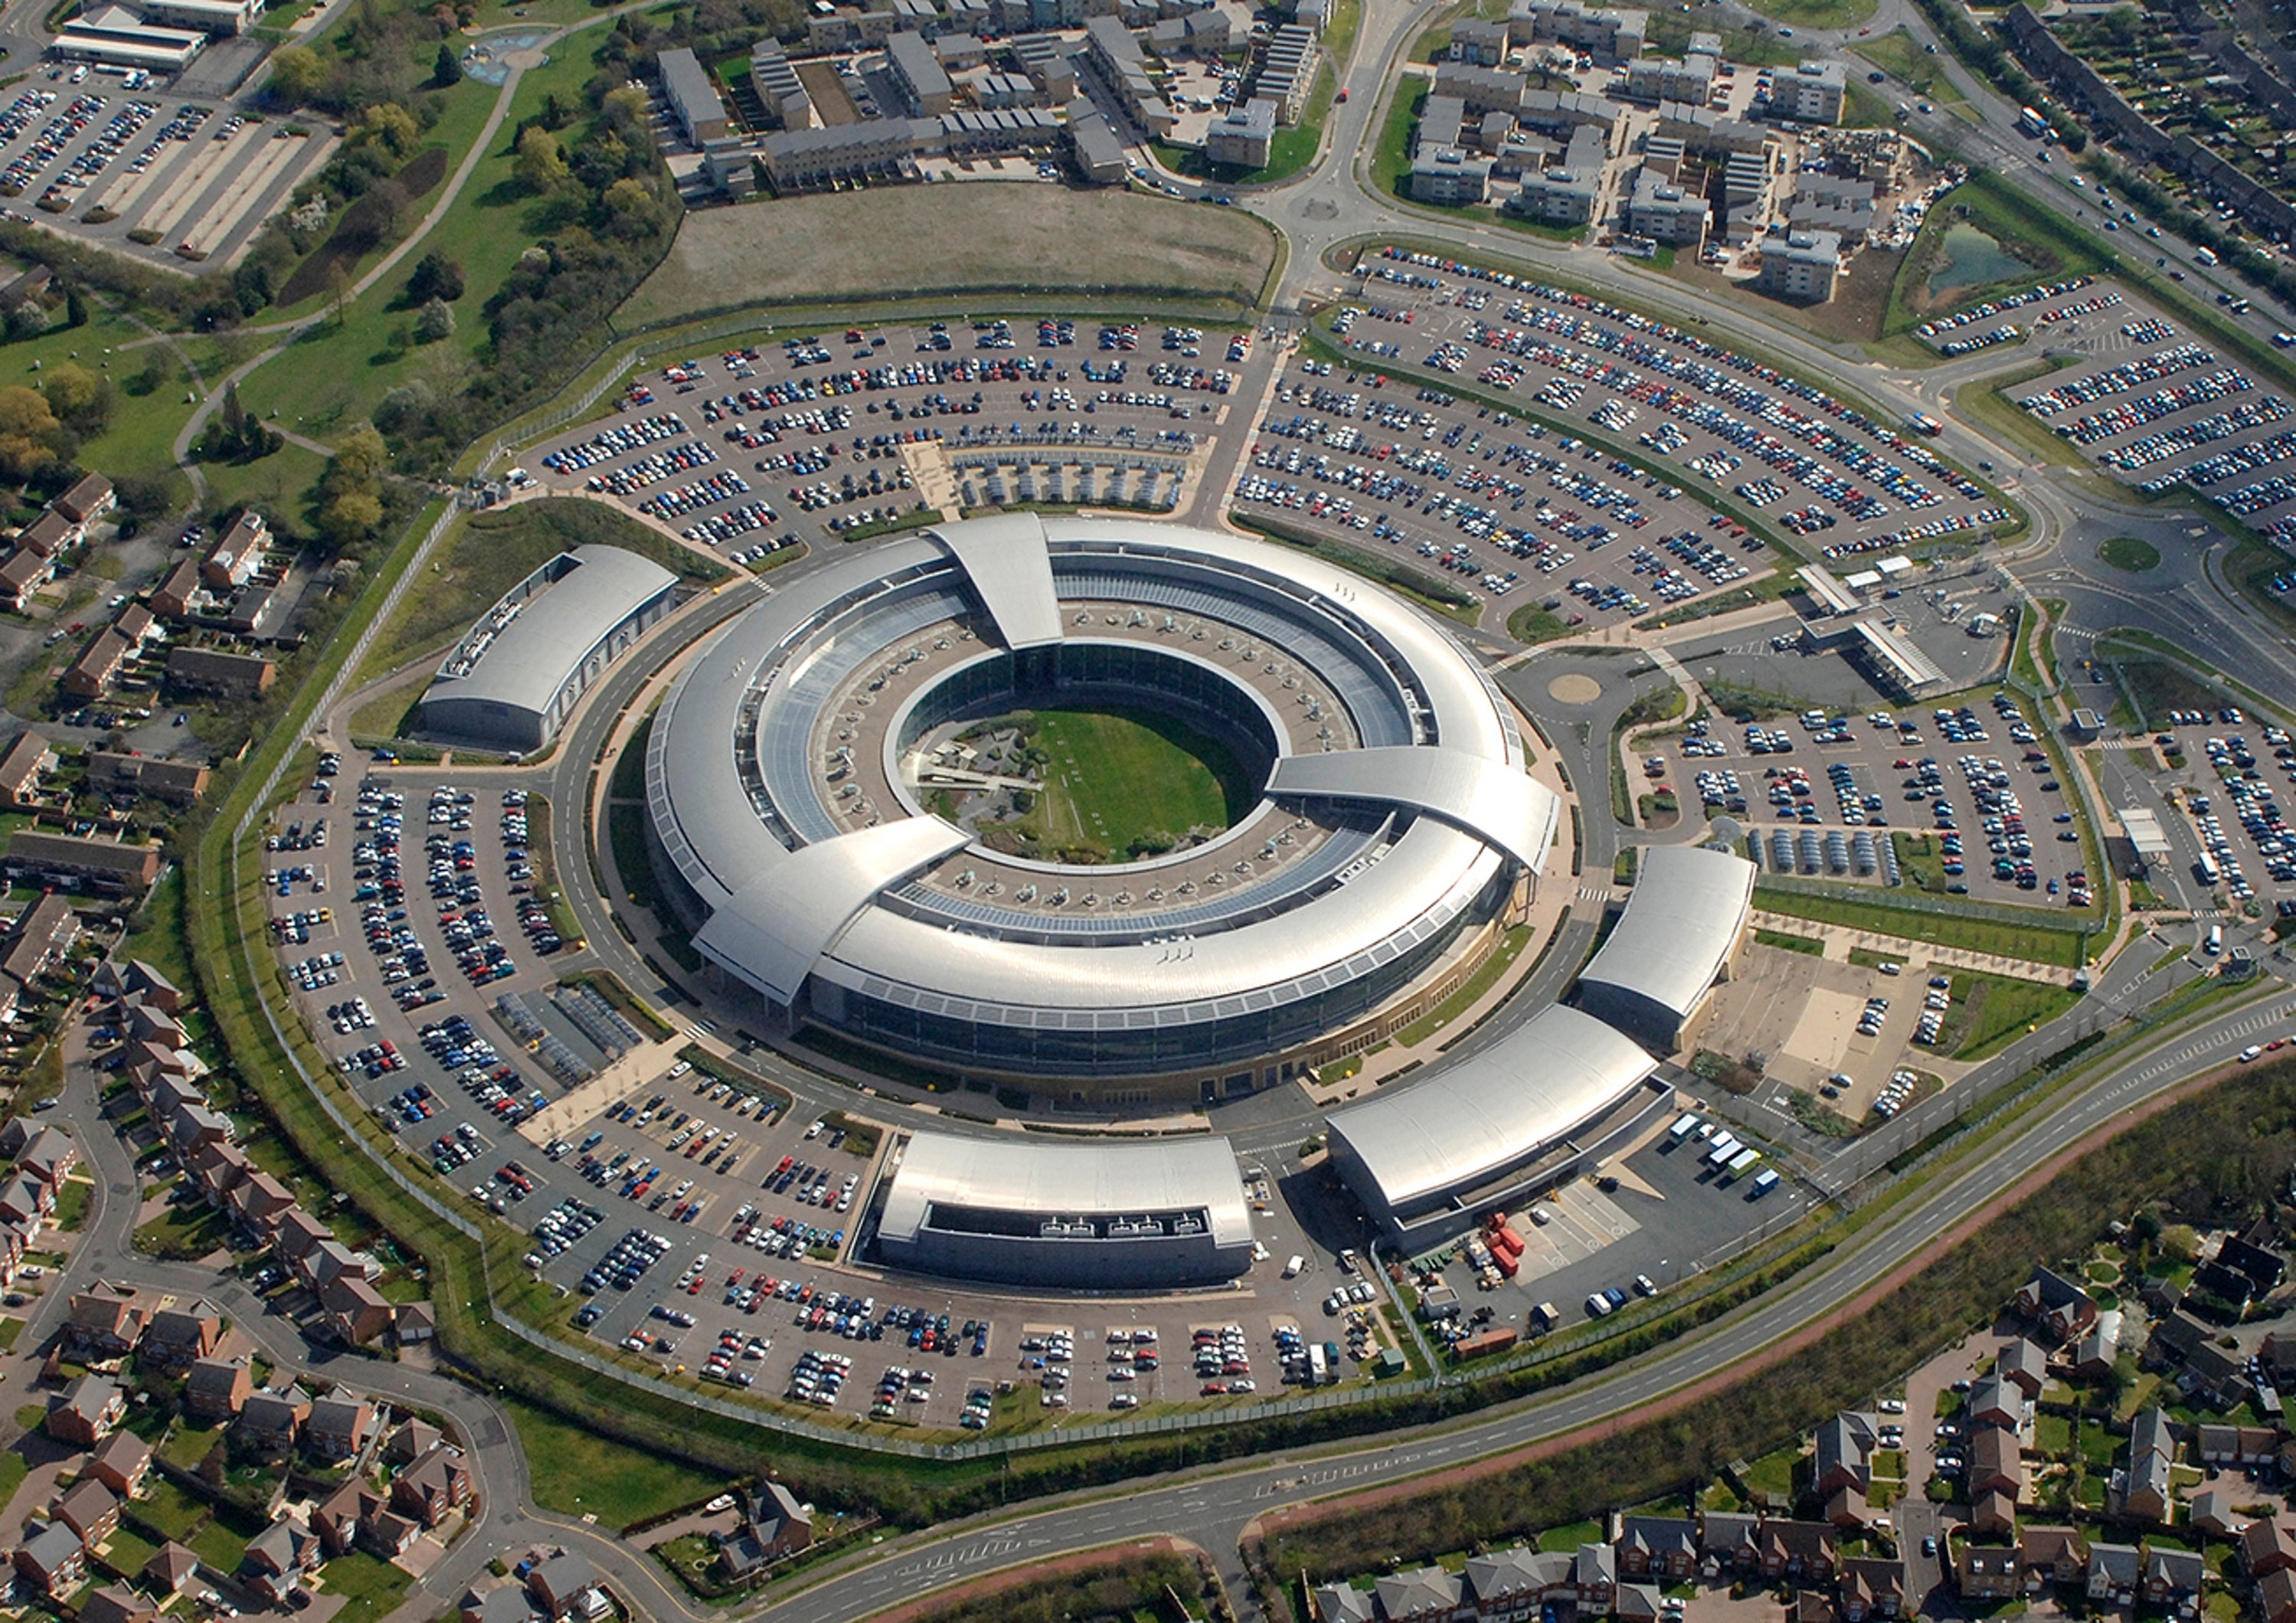
Paul Chichester, NCSC director of operations, said that the cyber campaign showed Iran’s ruthless use of digital surveillance to target dissidents.
“The details of this cyber campaign reveal how Iran ruthlessly uses digital surveillance in pursuit of its aim to repress critics of the regime, stealing emails and messages and accessing devices,” he said.
 open image in gallery
“With our international partners, we strongly encourage individuals at risk to familiarise themselves with the social-engineering techniques described in the advisory, and to act on the mitigation advice.
“We will continue to call out malicious cyber activity by the Iranian state and support communities with practical advice to strengthen their online personal security.”
The FBI issued its own advisory, and claimed the Iran government’s Ministry of Intelligence and Security (MOIS) was using the malware to “collect intelligence, conduct data leaks, and inflict reputational harm against their intended targets.”
Detailed technical advice about the malware was published on the NCSC website, as well as how to avoid falling prey to them.
Over the summer, NCSC chief Richard Horne warned that hostile states, such as Russia, China and Iran, were increasingly targeting the UK’s critical systems.
He said that three-quarters of cyber attacks impacting organisations within the UK’s critical infrastructure over the past year could be linked back to hostile state actors.
More about
NCSCjournalistsIntelligencemalwareFBI
Join our commenting forum
Join thought-provoking conversations, follow other Independent readers and see their replies
Most popular
Popular videos
Bulletin
Read next
Fonte: – World RSS Feed