Hackers target fridges in French supermarkets in ‘unprecedented’ cyberattack to spoil food
Por Suha Kidwai — – World RSS Feed
Hackers target fridges in French supermarkets in ‘unprecedented’ cyberattack to spoil food
Hackers target fridges across Intermarché, E.Leclerc, and Super U stores, reportedly causing millions of euros in food losses
Suha Kidwai Monday 12 October 2026 15:40 BST
- Bookmark
- Comments Go to comments
Bookmark popover
Removed from bookmarks
Close popover

Become an Independent member to bookmark this article
Want to bookmark your favourite articles and stories to read or reference later? Start your Independent Membership today.
Already a member?
Log in
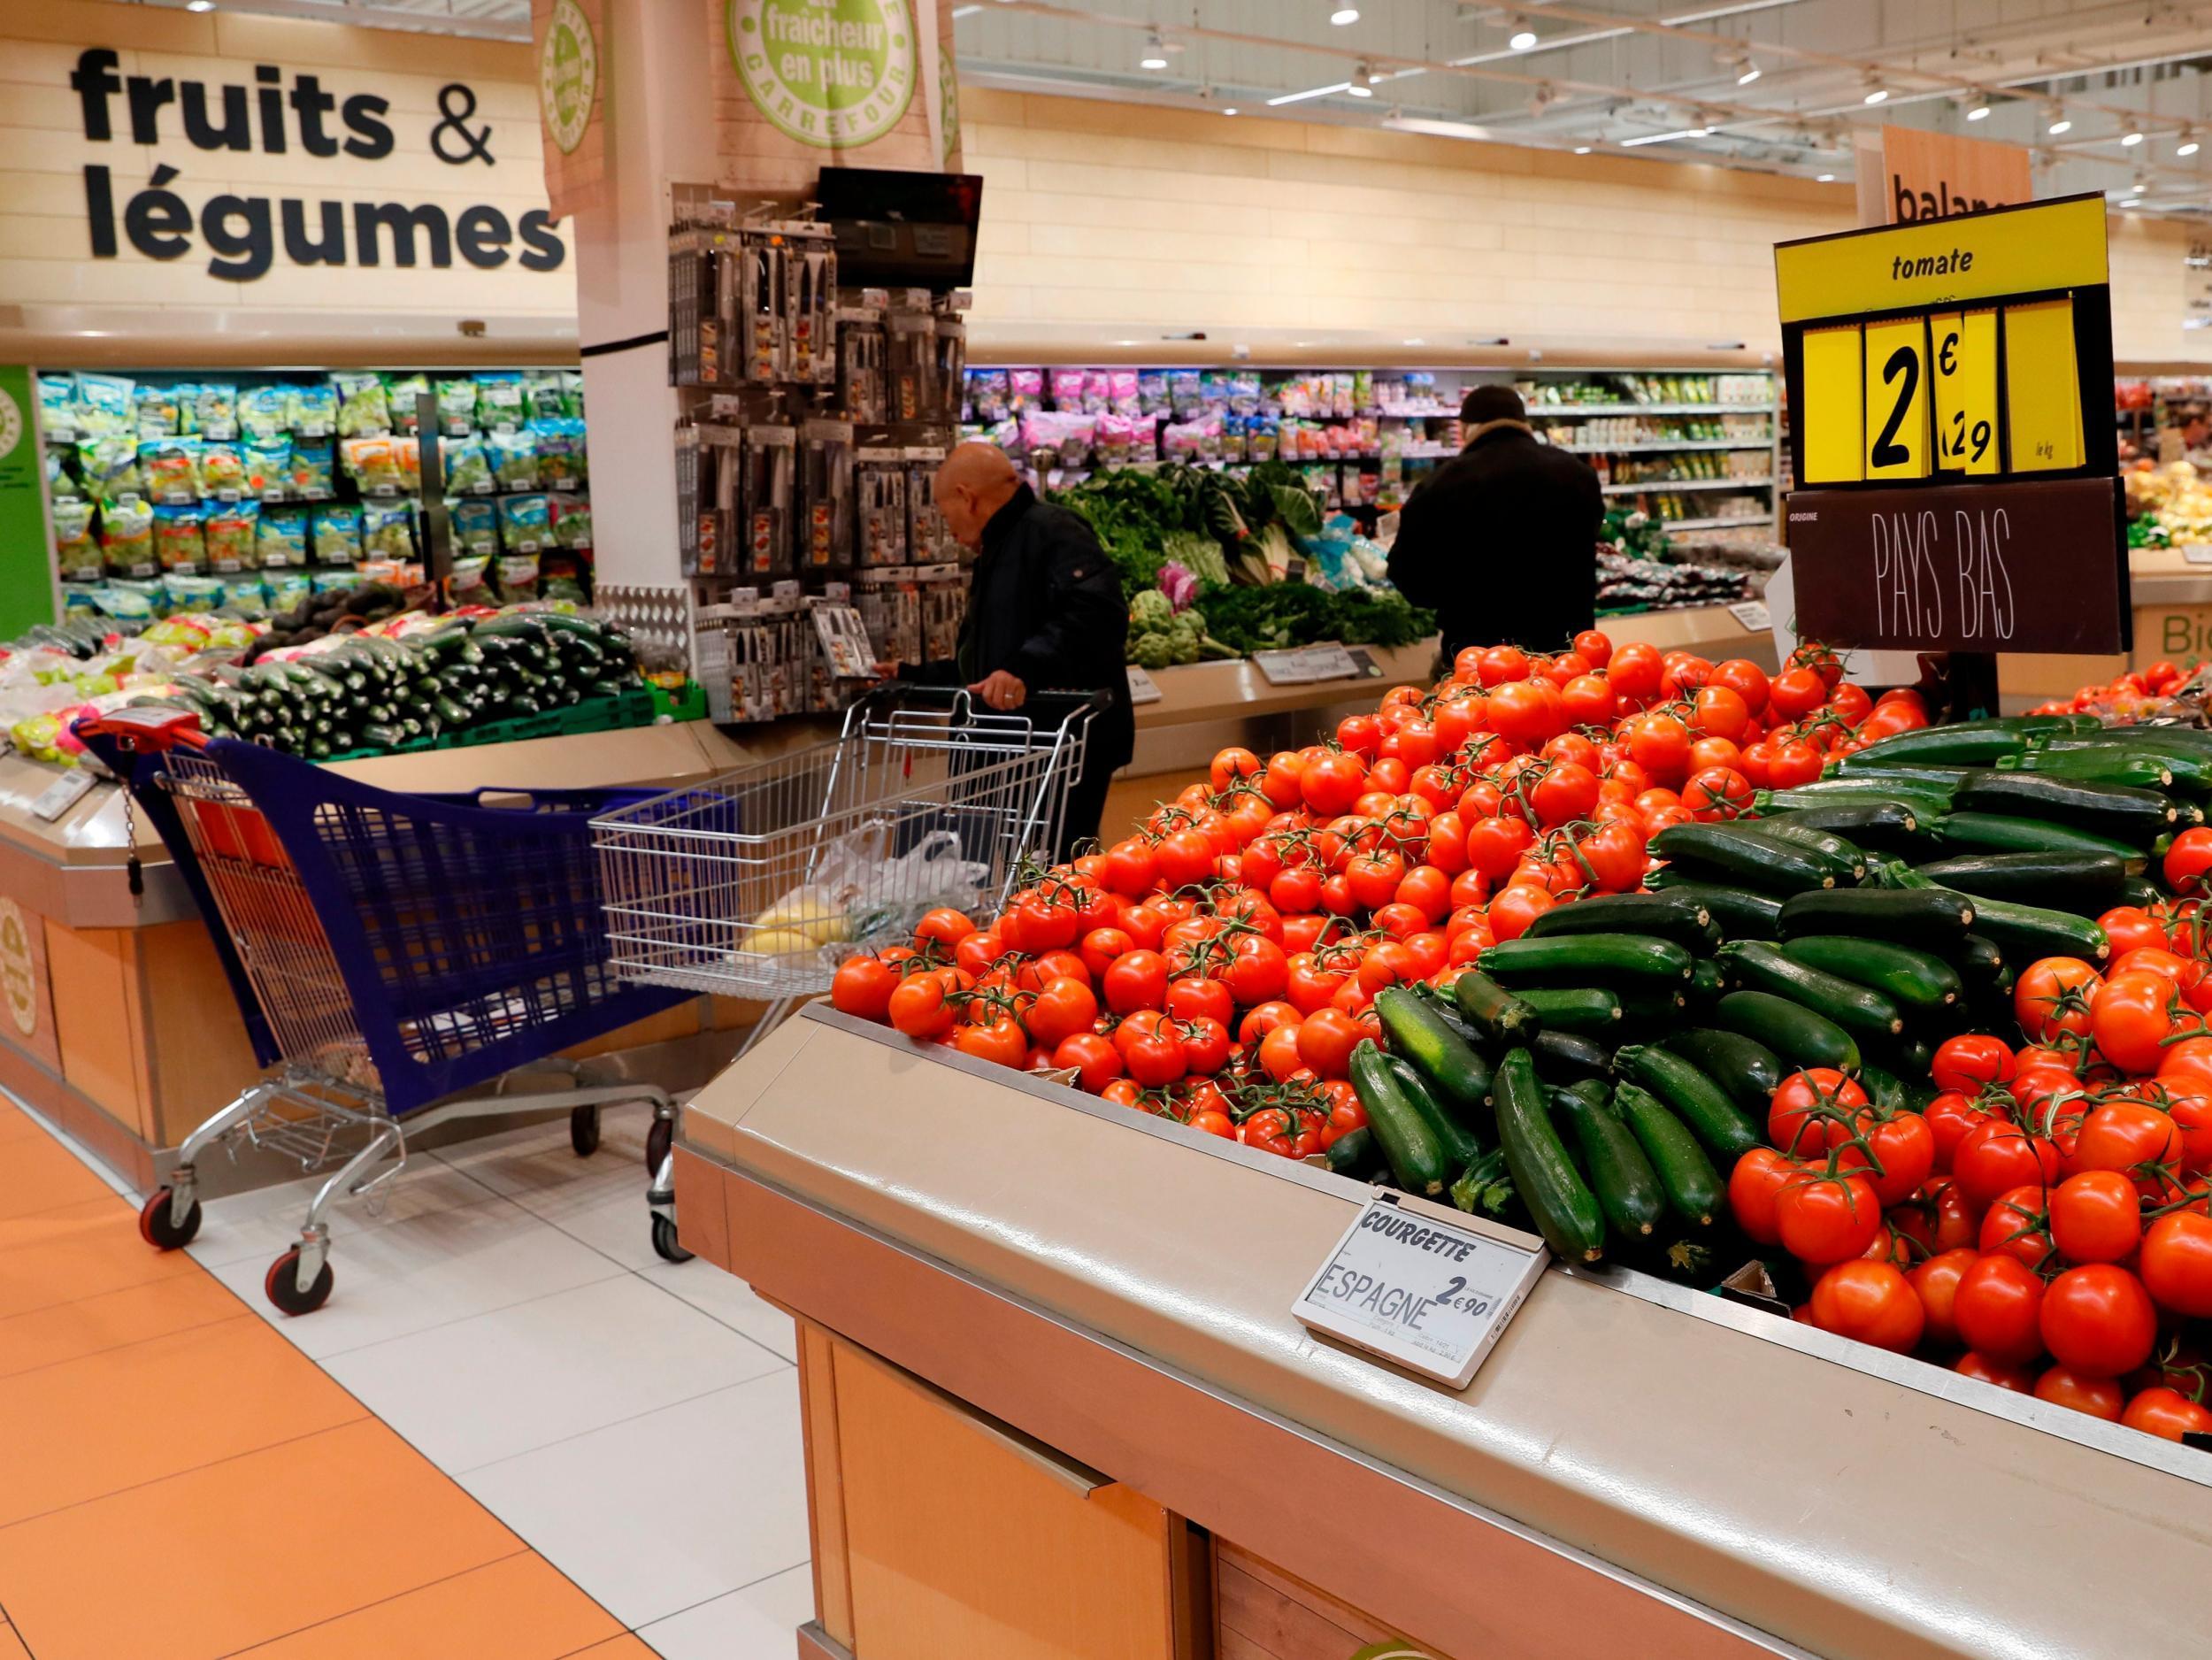
A major cyberattack targeting commercial refrigeration systems across France has left more than 150 supermarkets facing millions of euros in damages after hackers remotely altered fridge temperatures overnight.
The attack compromised cold-chain control software across nationwide locations of Intermarché, E.Leclerc, and Coopérative U (Super U).
Rather than shutting systems off, the attackers remotely reprogrammed cooling regulators to force a continuous defrost cycle, driving internal temperatures up to 50C.
Store workers arriving on Monday morning discovered compromised units left vast quantities of fresh produce, meat, dairy, and frozen goods completely spoiled.
Dominique Schelcher, head of Coopérative U, confirmed his retail network was among those hit, stating that technical teams are now working alongside specialists to restore normal operations.
Individual sites have reported severe inventory losses. An Intermarché and an E.Leclerc store in Haguenau, eastern France, estimated combined stock damages at €270,000 (£225,000), according to regional news outlet Sud Ouest.
Security experts have indicated the hackers exploited vulnerabilities in remote management software manufactured by cooling systems firm Danfoss.
Previous cyberattacks have targeted key infrastructure in France. In August, hackers breached the country’s internal tax agency systems, compromising income and property records for 678,000 taxpayers and businesses.
In early 2024, cybercriminals compromised third-party payment processors Viamedis and Almerys, exposing the personal data of 33 million healthcare policyholders across France, forcing pharmacies nationwide to temporarily revert to manual processing.
Together, the incidents highlight the growing vulnerability of French critical supply chains to third-party software breaches.
French law enforcement and national cybersecurity agency ANSSI have now opened an investigation to identify the origin of the supermarket attack.
More about
Join our commenting forum
Join thought-provoking conversations, follow other Independent readers and see their replies
Most popular
Popular videos
Bulletin
Read next
Fonte: – World RSS Feed